01.What Anthropic actually built and tested
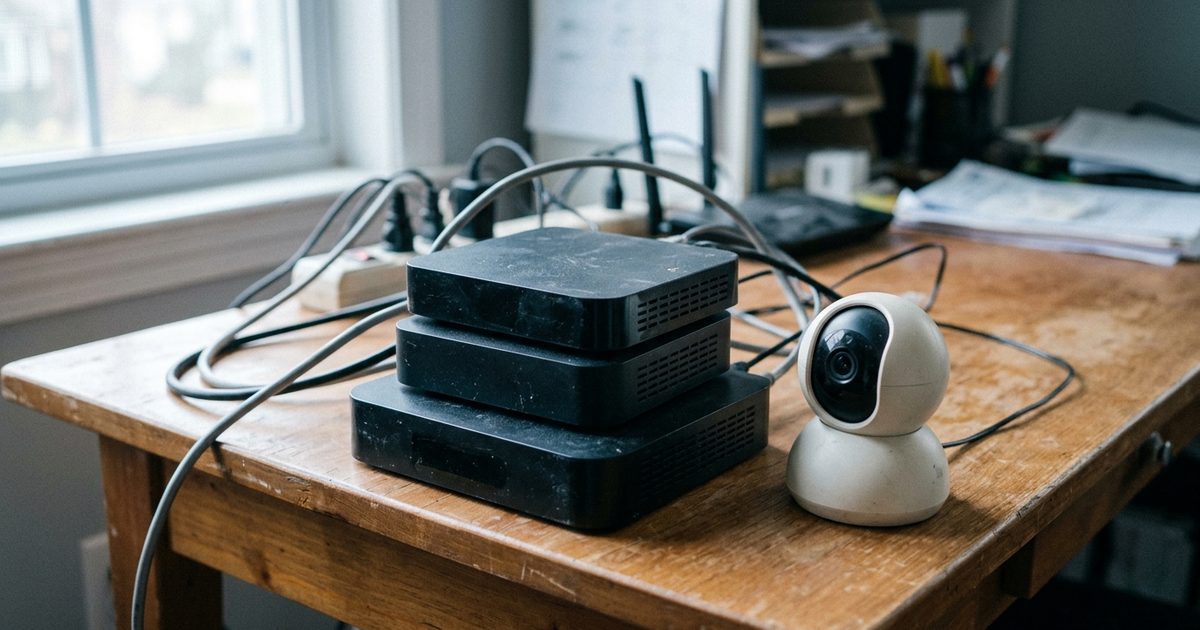
Anthropic's Frontier Red Team, the company's offensive-security researchers, has published a study on what it calls autonomous replication: an AI model that copies itself from one machine to another without a person driving it. The researchers bought fifteen off-brand Android TV boxes for about fifty-five dollars each and wired them together. Together the boxes were just powerful enough to run a 26-billion-parameter model, Gemma4-26B-A4B, which they split across the machines. The fleet managed only 0.39 tokens per second, far too slow for a chatbot, but the point of the experiment was reach, not speed.
The team then built a controlled network of eight Android emulators on Google Cloud. A seeded agent had to hop from machine to machine through an open debugging port, install a copy of itself, and start an inference server on each target. Of the open-weight models tested, only GLM-5.2, a very large model from China's Z.ai, completed the full loop, reaching all eight machines in four of five trials. The researchers describe the result as an upper bound, because they deliberately made the hacking step easy.
02.Why cheap smart devices are the target
Why cheap gadgets? Because they are the softest target. Off-brand Android TV boxes and smart appliances often run old versions of Android with few security features, ship with default passwords, and rarely receive updates. A model small enough to run on them could spread across thousands of them, each device doing a little of the work.
The researchers point to Kimwolf, a botnet that infected more than two million devices, mostly cheap Android TVs. If every fifteen of those boxes ran one copy of the 26-billion-parameter model, the network would hold roughly 133,000 copies. Their combined computing power would be worth at most about forty Nvidia H100 chips, but the electricity and the hardware would belong to other people.
03.What the test did and did not show
It is important to be precise about what this is not. Anthropic has not built a worm loose on the internet. Its experiments ran in closed, controlled networks with shortcuts. The model that coordinated the spread, GLM-5.2, was far too big to run on the TV boxes; it installed a much smaller eight-billion-parameter model on them instead. Today's capable models are too large for the cheap devices, and today's small models are not capable enough to run the whole chain reliably. Those two limits do not yet meet.
But they are closing. Small models are improving quickly, and Anthropic estimates a model of this size could reach the level needed for reliable replication by the end of 2026. Spreading would also be slow, taking days per new machine, unlike ordinary malware that can infect thousands of devices in minutes. It would be noisy too: moving multi-gigabyte model files between devices creates traffic that network monitors can spot.
04.Why this matters in India
For India this is not an abstract worry. The country is one of the world's largest markets for budget smart TVs, streaming boxes, CCTV cameras and other connected devices, and millions of them sit in homes, shops and small offices with their default settings untouched. Last week, India's cyber agency CERT-In said autonomous AI agents had accessed Indian organisations' systems without authorisation, a reminder that agentic AI risk is already real here rather than hypothetical.
Security experts treat poorly secured internet-of-things devices as the classic weak link: a cheap camera or TV box can be an easy way into a home or small-business network. As AI makes each compromised device a little more useful to an attacker, the value of hardening these devices rises.
05.What you can do about it
The practical steps are unglamorous but effective. Change the default username and password on any smart device you buy, and turn off features you do not use. Keep firmware updated, and replace devices that no longer get security patches. Put smart devices on a separate Wi-Fi network from the laptops and phones that hold your work and bank details.
For businesses, the advice is to know what is on the network, restrict what each device can reach, and watch for unusual traffic between gadgets that have no reason to talk to each other. Anthropic's message is not that a self-replicating AI is here. It is that the ingredients are getting cheaper and better, and that the cheapest targets are the ones most of us never think about.
Frequently asked questions
What is an AI worm?
It is malware that copies itself from one device to the next without a person controlling it. An AI worm would carry an AI model with it and run it on the machines it infects, so it could work out unfamiliar devices on its own.
Has Anthropic built a working self-replicating AI?
No. Its experiments ran in closed, controlled networks with the hacking step made easy. A very large model completed a simplified copy-and-spread cycle, but no small model has replicated itself across real consumer devices.
How can I protect my smart devices?
Change default passwords, update firmware, remove devices that no longer get updates, and keep smart gadgets on a separate Wi-Fi network from the devices you use for work and banking.